Trusted by 3 500+ teams
icon-google
4.7/5

Build credibility your vendors can't break

Every digital asset firm runs on third-party software it doesn't control. When a vendor fails, the outage, frozen withdrawals, and headlines are yours to deal with. Codekeeper keeps verified copies of your off-chain stack in escrow, so they're ready to launch internally whenever you need it.

shield-check
ISO 27001 certified
handshake
10+ years of service
globe-lock
AES-256/512 encryption
hero-homepage

logo-partner-airbus-white
logo-partner-axxiome-white
logo-partner-bat-white
logo-partner-bayer-white
logo-partner-eu-parliament-white
logo-partner-general-motors-white
logo-partner-gorenje-white
logo-partner-intuit-white
logo-partner-louis-vuitton-white
logo-partner-nasa-white
logo-partner-nascar-white
logo-partner-pepsico-white
logo-partner-pfizer-white
logo-partner-pwc-white
logo-partner-nestle-white
logo-partner-siemens-white
logo-partner-slate-digital-white
logo-partner-airbus-white
logo-partner-axxiome-white
logo-partner-bat-white
logo-partner-bayer-white
logo-partner-eu-parliament-white
logo-partner-general-motors-white
logo-partner-gorenje-white
logo-partner-intuit-white
logo-partner-louis-vuitton-white
logo-partner-nasa-white
logo-partner-nascar-white
logo-partner-pepsico-white
logo-partner-pfizer-white
logo-partner-pwc-white
logo-partner-nestle-white
logo-partner-siemens-white
logo-partner-slate-digital-white

Your reputation is riding on someone else's stability.

Every vendor you depend on is a counterparty bet: that someone else stays funded, secure, and live. Right now you're holding dozens of those positions with no view of the odds. One wrong bet, and you pay in downtime and credibility.

In crypto, you can't reclaim lost trust

Your business lives on the confidence of its users, partners, and institutions. One public incident and all faith is gone. Nearly 80% of hacked firms never fully recover after their credibility is injured. Codekeeper gives you verified, tested proof of your resilience, so there's never any doubt in your service stability.
You're probably not as decentralized as you claim

You run on the same handful of cloud, node, custody, and oracle providers as everyone else. When one goes down, half the industry goes down with it. Decentralization built your industry, but it isn't yet an operational truth. With verified copies of your vendors' software in escrow, it can be.

The attack surface around your blockchain is massive

Most crypto theft never touches the chain. It comes in through a poisoned update, a compromised dependency, malicious code inside a product you trusted. Once it's in, everything that vendor touches is suspect. With an uncorrupted copy in escrow, you can cut the infection out and keep your systems running.

Unproven resilience is an all-around dealbreaker

Institutional clients stall deals over exit and portability in due diligence. Regulators go further: DORA requires a tested exit strategy per vendor, and MiCA decides if you operate in the EU at all. Different gatekeepers, one demand: continuity proof. Our Software Resilience Certificate gives you exactly that.
what-is-software-escrow

What is software escrow?

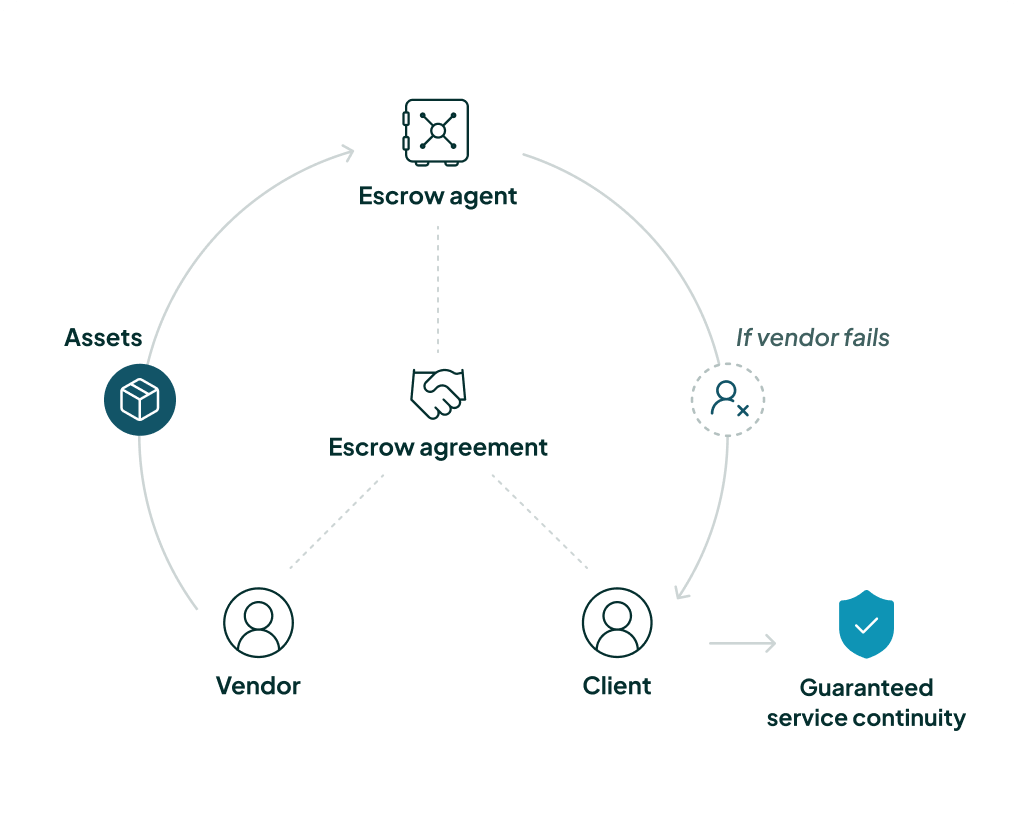
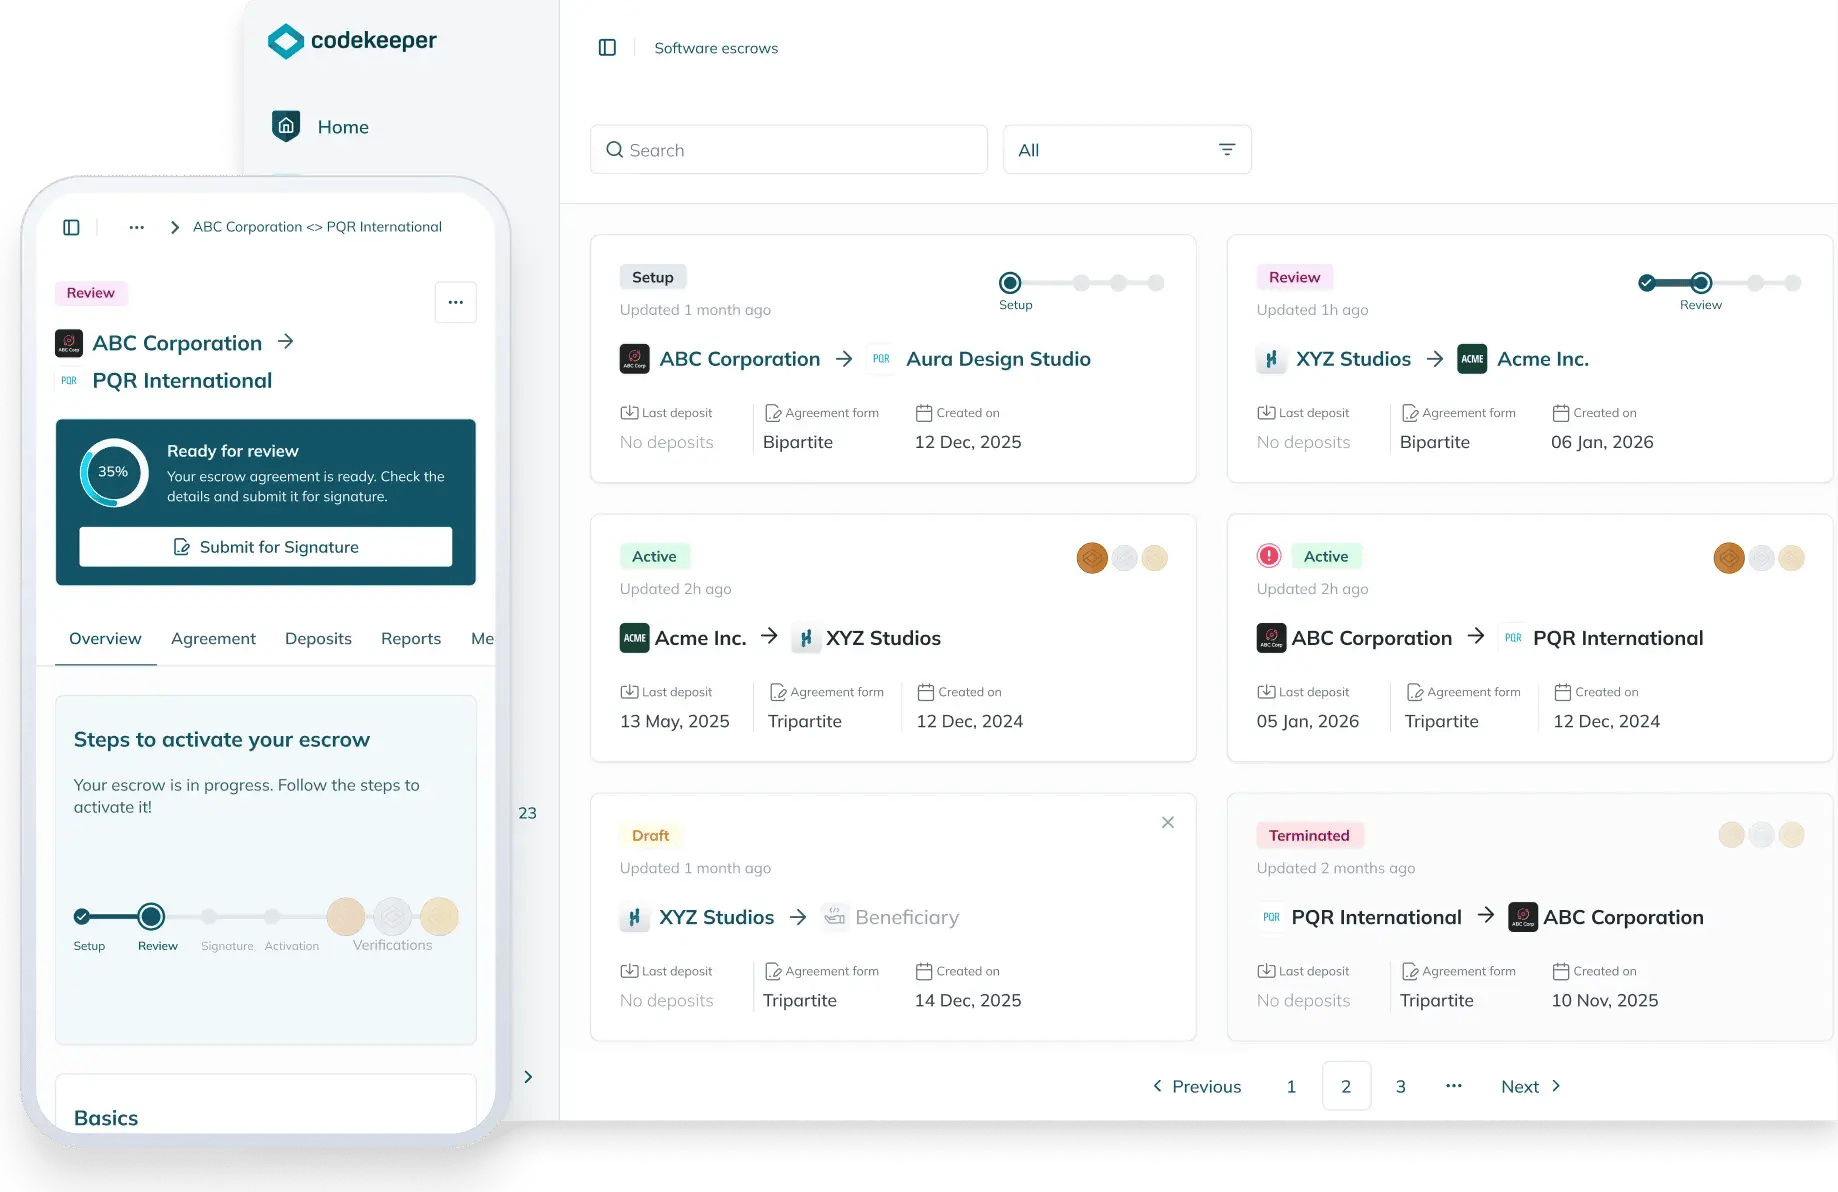
Software escrow is a mirror of the software assets you rely on. Source code, configurations, data, documentation, all of it. Your vendor deposits copies with a neutral third party, Codekeeper, and automated syncs keep everything current in an encrypted vault. If that vendor ever folds or kills the product, you launch your copy and run it yourself. Your chain already protects itself. This protects everything around it.

BE THE EXCEPTION WHEN THE INDUSTRY GOES DOWN

Stay live through any major outage

You saw the shared dependency for what it was and built your way out. Now the systems everyone runs on can fail without taking you with them. While the rest of the market posts apologies, no one on your platform even notices there's an issue. Your name quickly becomes synonymous with reliability.

be-the-exception-when-the-industry-goes-down
stop-inheriting-your-vendors-breaches
STOP INHERITING YOUR VENDORS' BREACHES

Quarantine the vendor, not your operations

You kept clean versions of every critical system on ice. The day a dirty update lands, you cut the vendor loose, bring up your own build, and keep serving users while they handle the fallout. What ends other platforms becomes a line in your changelog.

TURN SCRUTINY INTO YOUR SALES PITCH

Satisfy institutional vetting on the first pass

You stress-tested your continuity and put the results in writing. Now exit and portability is the fastest section in any vendor review, and a regulator's request is just a forwarded attachment. Deals that stall for your competitors close on schedule for you.

turn-scrutiny-into-your-sales-pitch

How it works

A continuity layer sounds like a quarter-long engineering project, but it doesn't have to be. There's no code to change, no sprint to plan, and no hard sell to your vendors. Three short steps, and we take care of the rest.

1

1.  Book a free 30-minute call.

We'll map the software behind your operation together and recommend the right coverage for your needs.

2

2.  Pick what fits your business.

Once you've chosen a resilience solution that suits your setup, our legal team will draft your agreement within one to three days.

3

3. Invite your collaborators.

Your vendors link their systems through any of our 50+ integrations. We'll verify the deposits and issue your Software Resilience Certificate.

You get dedicated support at every step.
Book a demo
"Codekeeper lifted us at every turn, from setting up the escrow agreement, handshaking the agreement with all parties, and using the tool to get the repositories in sync. I'd spotlight the portal that walks you through each step — it builds trust for us and our clients alike — plus the technical setup that enables our teams to share code effortlessly. That combination simplifies everything and saves us real effort."
Paul T. *
Senior Managing Director
* Pseudonym used to maintain customer confidentiality.

If your trustworthiness depends on your resilience, activating software escrow is the right decision.

A digital asset business spends years earning its standing, then stakes all of it on software it will never control. When a vendor goes under, the market doesn't ask whose fault it was. With software escrow in place, a collapse stops at the vendor's door, and you restore service without them. Set it up before a DORA or MiCA audit outs you as unreliable.
  • Live through any outage.
  • Clean after any breach.
  • Credible to any institution.
shield-check
ISO 27001 certified
globe-lock
3 500+ protected teams
handshake
10+ years of service
cta-ready-for-continuity-bg-compressed
Frequently asked questions

Good questions to ask first.

Does software escrow touch our funds or smart contracts?

No. Software escrow only covers conventional software: source code, configurations, data, and documentation for your operational systems. We never hold wallets, private keys to client funds, or anything deployed on-chain. Your treasury and your smart contracts sit completely outside the arrangement.

We already pay for smart-contract audits. Doesn't that cover us?

No. A smart-contract audit reviews your on-chain code for vulnerabilities at a point in time. Software escrow covers a different layer: the off-chain vendor software your operation runs on, so you keep access to it if a vendor shuts down or drops support. One doesn't replace the other; they cover different layers of your technology.

We're multi-region and partly decentralized. Why would we need this?

Multi-region infrastructure protects you against outages, and you should keep it. It can't help when the vendor itself fails: if a provider shuts down, is acquired, or pushes a compromised update, every region runs the same software from the same source. Software escrow covers that scenario by giving you your own copy to recover from, independent of what happens to the vendor.

Most of our stack is open-source. What's left to escrow?

Quite a lot. Public repositories can be deleted, abandoned, or taken over, so software escrow can include snapshots of the open-source code you depend on. The open-source code is also only part of your setup: your configurations, deployment scripts, integrations, and the proprietary vendor products around it aren't public at all. Software escrow keeps all of it together, so you can restore a complete working environment, not just the code.

We already have a documented exit strategy for DORA. Isn't that enough?

Not on its own. DORA requires exit strategies for critical vendors to be both documented and tested, and a written plan only meets the first requirement. Software escrow gives you the practical basis for the second: current deposits of the vendor's software that recovery can actually be carried out from, plus a Software Resilience Certificate you can show an examiner as evidence.

Will our vendors actually agree to this?

Yes. Software escrow is a standard request in enterprise software contracts, and established vendors are familiar with it. Our agreements are designed to work alongside your existing contracts without renegotiating them; our legal team drafts everything, and we handle the setup conversation with your vendor directly.

Let's build bulletproof software resilience together.