Palo Alto Networks Unit 42 has traced a prolonged intrusion at a telecommunications managed service provider, beginning September 2024, that ended in a memory-resident implant nobody had seen before. The actor, tracked as CL-STA-0954, first exploited CVE-2024-47575 — FortiJump — to compromise a FortiManager appliance, walking off with running configs, cryptographic trust material, and database files covering more than 500 managed FortiGate firewalls across the provider’s own infrastructure and its clients’ networks.
That haul bought the access for everything after. Using stolen credentials and a privileged foothold, the attackers later exploited CVE-2025-61624, a path traversal flaw in the FortiOS command line that Fortinet rates Medium at CVSS 6.0 and patched in April 2026. Exploiting it needs local access and high privileges already in hand, which the FortiManager archive supplied.
PEERSTITCH itself leaves no binary on disk, opens no listening ports, and makes no outbound connections. It injects into two legitimate FortiOS daemons, miglogd and iked, and builds a communication bridge between them inside process memory. When a VPN session arrives carrying the attacker’s marker, the iked hook takes an alternative path and skips FortiOS’s default validations — for that session alone. Unit 42 calls it resistant to conventional endpoint and network detection.
Fortinet’s fix is FortiOS 7.6.5 or 7.4.10 and above, with 7.2, 7.0, and 6.4 needing migration to a supported release. FortiProxy, FortiSwitchManager, and FortiPAM have their own fixed builds, and a virtual patch shipped in FMWP database update 25.120.
Source: The Hacker News
Researchers at the University of Toronto’s Citizen Lab have uncovered a disturbing new surveillance technique: online ads being used to silently install spyware — no clicks required. They call it AdFection, and say it’s the first confirmed case of mercenary spyware delivered through targeted ads.
At the center, according to the report, is Israel-based Discover-Tech, which calls itself an advertising agency and runs a platform called Controlium. When a user is shown one of its seemingly benign ads, their advertising ID and IP address are sent to Discover-Tech’s servers. If they’re flagged as a target, malicious code is pushed to their device within seconds — invisibly. Citizen Lab found no sign the company does any legitimate advertising.
Citizen Lab says with high confidence that at least 45 Al Jazeera devices were infected this way with spyware from Candiru. Discover-Tech’s ads were also shown on networks at the UN, NATO, and EU institutions, and partner firm Confiant found them on ICC and IAEA networks. An ad impression alone doesn’t prove infection, but researchers say those networks need urgent investigation.
Google and IAB Europe have since dropped Discover-Tech from their certified vendor lists, and Google and Beeswax have cut off its ad access. Researchers are now calling on regulators and lawmakers in the US, Europe, and beyond to investigate the companies involved.
Source: The Guardian
CenterPoint Energy has confirmed that a data breach exposed personal information belonging to 1M+ Texas residents, according to a filing posted to the Texas Attorney General’s breach database on October 13. The Houston-based utility first disclosed the incident to the SEC on September 14, two days after a hacker bragged on a cybercrime forum about stealing nearly 7.5M customer records, a figure CenterPoint has not confirmed.
Compromised data includes names, addresses, Social Security numbers, and driver’s license numbers. The hacker also posted a 2.5GB archive on September 12 allegedly containing around 3M phone numbers. CenterPoint says only a portion of its customers were affected and that electric and gas delivery was not disrupted, but it also serves Indiana, Minnesota, and Ohio, and the total impact remains unclear.
Notably, CenterPoint hasn’t sent notification letters to impacted individuals yet. The company says it is still working with outside experts to determine which customers will be notified.
Source: SecurityWeek
Microsoft and Japan’s National Police Agency announced a takedown of Yam Store on October 14, a Chinese-language cybercrime marketplace tracked as Storm-3119. Yam Store never sent a phishing message. It sold the infrastructure: hijacked Microsoft and Google accounts, licenses, and storage, found by automated scanning for expired organization names and resold wearing the legitimate customer details attached to them.
Its customers did the sending. Microsoft groups the developers of three kits — CoGUI, Haozi, and Iron Man System — as Storm-2990, and says the actors behind them have pushed over one billion phishing emails and SMS messages at more than 75 000 organizations across 150 countries since January 2026. Iron Man System alone carries 2 335 templates aimed at 139 countries, and only reached Yam Store in June.
Acting on a US court order and working with Resecurity, Cloudflare, Oracle, Proofpoint, and others, Microsoft has disabled over 20 000 tenants and 140 000 malicious domains.
Resetting passwords won’t finish the job. Andrew Costis of AttackIQ points out that an application has its own identity and permissions, so access granted to one during an attack survives a password change. Corsica Technologies CISO Ross Filipek adds that device code phishing lands victims on genuine sign-in pages, which is why training people to check where a link goes doesn’t catch it.
Source: Dark Reading
Two Americans — Michael Bostelle of Pennsylvania and Juan Pena Carrillo of Texas — have been arrested on charges of wire fraud, money laundering, and identity theft. Prosecutors say they helped run laptop farms: US homes where employer-issued laptops sit plugged in and loaded with remote-access software, so workers in North Korea can log in and look US-based.
The indictment charges 14 people in total — the two arrested, ten in China, and two whose names stay sealed. The scheme ran from 2019 to July 2025, allegedly generated over $3 million, and placed workers at more than 70 US companies in communications, cyber support, healthcare, manufacturing, and retail. The FBI estimates North Korea keeps 85% to 90% of what they earn and spends it on weapons programs.
FBI agents searched 40 Texas homes between September 21 and 25 under Operation Lonestar Roundup, seizing 187 laptops and the switches used to drive them remotely.
The FBI wants identity checked from the job application through to the last day of employment, and flags remote monitoring software on company machines, downloads unrelated to the role, and bank accounts and home addresses that keep changing.
Source: SecurityWeek
Kim Jong-Un sent roughly 14 000 to 15 000 troops to fight alongside Russia in October 2024, and Proofpoint suspects Moscow never gave Pyongyang a timetable for getting them home. So North Korea appears to have gone to the other side of the front for answers. Hackers linked to the DPRK have been spear-phishing Ukrainian government officials, academics, and policy experts, and Genians Security Center assesses the campaign went looking for casualty numbers, how prisoners are being handled, and what happened to the two North Korean POWs Ukraine transferred to South Korea in September.
Those targets don’t open attachments from strangers, so the first email doesn’t carry one. No link either — just a credible greeting built to earn a reply and slip past email filters. One attack began on August 6, 2026, with an email impersonating the organizers of a Seoul security conference. Answer it, and the follow-up arrives: a malicious LNK file wearing a PDF icon and a double extension.
Patience is the whole technique, and it only half works. Recent attempts have been littered with errors, including emails inviting victims to Google Meet calls that contain Zoom links instead, and Genians says most of the observed attempts failed. Proofpoint’s Greg Lesnewich says the group takes little effort to hunt — the pace and volume are what wear defenders down.
Source: Dark Reading
A cyberattack hit French supermarkets overnight on Sunday, October 11, with hackers remotely triggering the forced-defrost function built into store refrigeration controllers and leaving it running. Fridges and freezers climbed to 50°C. Managers found the damage on Monday morning, and the French government now puts the count at around 700 stores.
France’s cybersecurity agency says the compromises involve remote-control modules from Danish firm Danfoss and US firm Copeland. Danfoss says the affected units were older models whose security software couldn’t be updated, and that it has long told customers to keep supported systems current.
Chains hit include Coopérative U, Intermarché, Carrefour, and Monoprix, with E.Leclerc affected through one of its refrigeration suppliers. Intermarché disconnected around 100 further stores from the internet to stop the same thing reaching them. Two stores in Alsace alone reported €270,000 in losses, with nationwide damages expected to reach millions. Some locations reported small fires.
French prosecutors have launched a cybercrime investigation, and the European Food Commissioner warned that “weaponisation of food has become a reality.”
Source: BBC News
On-chain investigator Specter estimates losses may top $86 million from a supply chain attack on Ledger hardware signers sold through Southeast Asian reseller CryptoBilis. Ledger’s Donjon security team confirmed an unauthorized hardware implant inside one affected user’s device, and says it hasn’t confirmed how many users were hit or how much went missing.
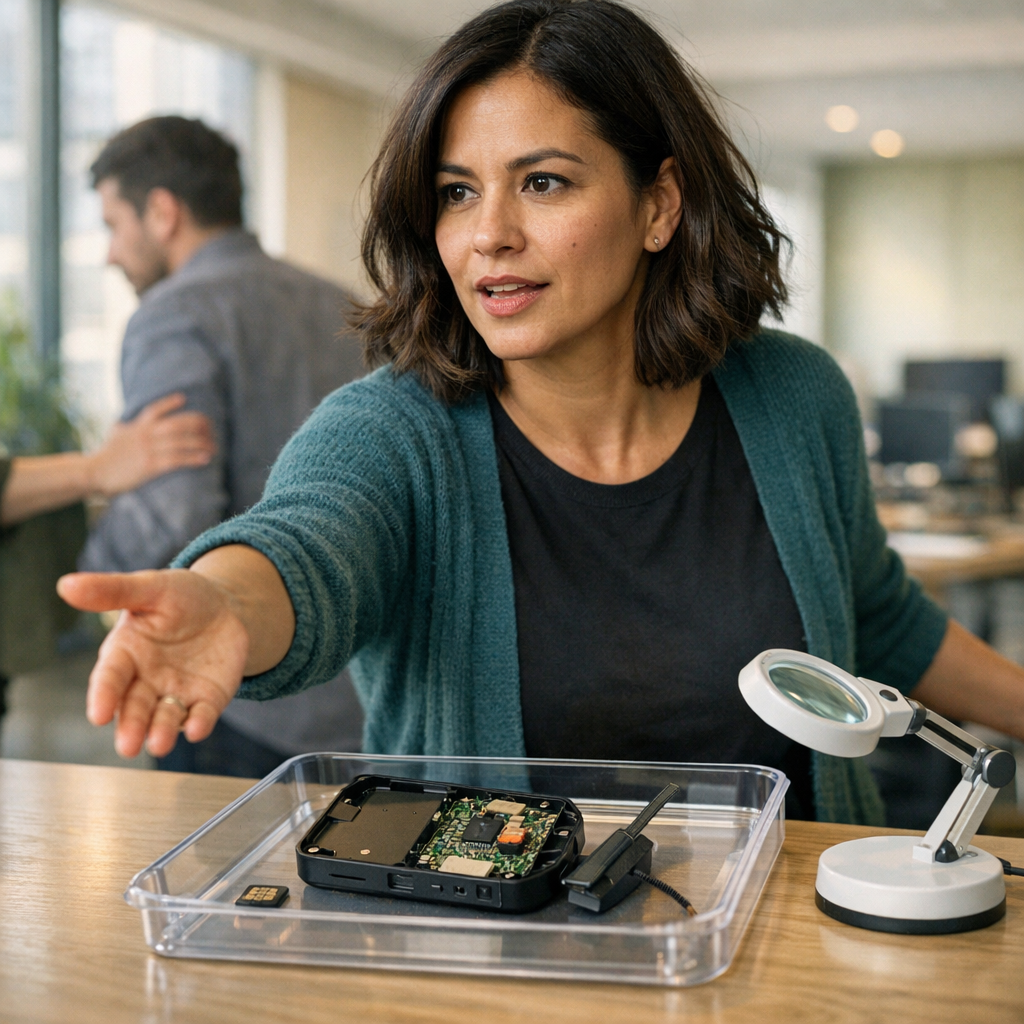
Someone along the distribution chain appears to have soldered a small circuit board inside the enclosure, under the screen. The implant reads the 24-word recovery phrase as the signer displays it during setup, then transmits it over LTE using a built-in eSIM — giving attackers full access to victims’ wallets.
Disclosed on October 9, the theft was pinned to CryptoBilis-sold units immediately, and every confirmed loss so far involves one. Ledger tells anyone who bought from the reseller in the last 90 days and hasn’t started setup to leave the device alone; anyone who has set one up should move assets to a new signer with a new seed.
Source: SecurityWeek
SonicWall’s SMA 1000 appliances carry a flaw that scores a perfect 10.0 on CVSS, and attackers began probing for it two days after the fix shipped. CVE-2026-102255 is a pre-authentication server-side request forgery bug in the WorkPlace portal. SonicWall says an unintended access path lets a remote, unauthenticated attacker direct the appliance to issue requests on the attacker’s behalf and reach internal functionality.
The advisory landed on October 6, with SonicWall saying at the time there was no evidence any of its four flaws had been exploited in the wild. Defused logged unauthenticated SSRF traffic against its SMA decoys from October 8, and Previdian reported attempts on its sensors the next day. Benoît Sevens of Anthropic reported the flaw; technical details have not been published.
Upgrade the 6210, 7210 and 8200v to 12.4.3-03670 or 12.5.0-03082. September’s platform hotfixes, 12.4.3-03526 and 12.5.0-02952, are still vulnerable, so patching last month doesn’t cover you. There’s no workaround. SSL-VPN on SonicWall firewalls and the SMA 100 Series are unaffected.
Source: Dark Reading
Oleg Korniev, 42, a dual Ukrainian-Russian citizen, pleaded guilty on October 8 to helping lead Your Mule Cashout (YMCO), a massive money laundering network serving cybercriminals. YMCO recruited over 15 000 Americans as money mules through spam emails from fake companies, putting each one through a hiring process that looked real and telling them they would process payments for legitimate businesses. They were moving stolen funds to Eastern Europe, and they were never paid.
Cybercriminals paid YMCO a cut of whatever it moved. The network laundered at least $10 million from 750-plus US bank accounts, and Korniev ran it like a company: writing the procedures, hiring and firing staff, and rewarding or punishing them on performance.
Korniev admitted YMCO was responsible for over $14.7 million in actual and intended losses to confirmed victims, and that he intended to launder over $9.7 million and did launder at least $7 million. He pleaded guilty to five counts covering money laundering, computer fraud, access device theft, and aggravated identity theft, and faces two to 50 years. Four co-conspirators were extradited to the Western District of North Carolina before him and pleaded guilty, reportedly drawing 37 to 63 months each.
Source: SecurityWeek