<img height="1" width="1" style="display:none;" alt="" src="https://px.ads.linkedin.com/collect/?pid=10643465&amp;fmt=gif">

Fake Recruiters Infected 30,000 PCs in a $10.7M Crypto Theft

Hackers posing as recruiters tricked developers into running malicious coding tasks, using AI face swaps on video calls and draining 7,000 crypto wallets.
Content Team

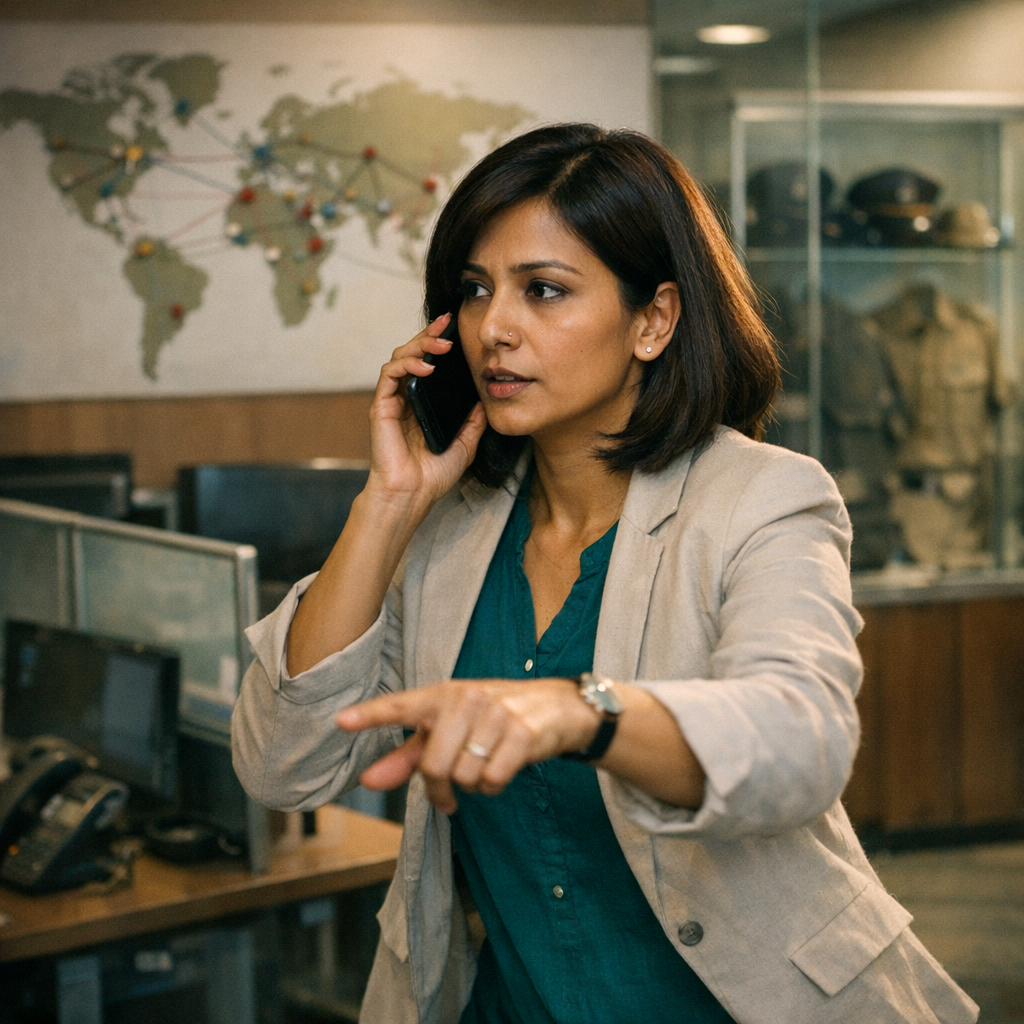
The FBI's Cyber Division, with Japanese, Australian, and German authorities, warned on September 18 that a North Korea-linked group tracked as WaterPlum — also called Contagious Interview — infected more than 30,000 personal computers across 100-plus countries between December 2025 and July 2026. Posing as recruiters on job boards, social networks, and freelance platforms, they got developers to run malicious files as fake coding tasks.

Some used AI face-swapping software to appear as the recruiter on video calls, then cut the camera a few minutes in, blaming network trouble. The payloads include BeaverTail, InvisibleFerret, OtterCookie, OtterCandy, and StoatWaffle, which between them steal credentials, wallet keys, and project files. Authorities put the haul at 7,000 cryptocurrency wallets and $10.71 million moved to North Korea.

A compromised developer is also a route into their employer's network, which is what lifts this above an individual problem. Run code from a recruiter only in a sandbox or virtual machine, never on a machine holding personal data or wallets. If you find an infection, disconnect immediately and assume the data is already gone.

Source: Cyber Security News

Share this article
Share on facebook Share on linkedin Share on twitter Share on email
blog_book_a_demo_cta_3x
Have questions about protecting your software?
Our escrow experts are standing by to help.
Book a free demo