European Union


 Global standards


 US

 UK

 Australia

 Netherlands

Ticker feed
A cyber-espionage group called Bitter, also tracked as TA397, is targeting organizations across South Asia with an upgraded version of its custom remote access Trojan, PapRAT, FortiGuard Labs reported on November 2, 2026. Active since at least 2013 and linked to India, Bitter has historically gone after government, energy, and engineering targets.
Bitter rewrote PapRAT in Rust, moving it off C++ and adding PowerShell execution plus sleep and exit commands for 11 in total. The group runs three infection chains built on legitimate Windows features. One abuses ftp.exe and scheduled tasks without deploying any malware binary. In another, PapRAT pulls down a second implant, WmRAT.
Sectigo senior fellow Jason Soroko notes that wiping PapRAT from that chain’s victims may leave the attackers inside, so defenders should also hunt for leftover scripts, scheduled tasks, and extra payloads.
Source: Dark Reading
A cyber-espionage group called Bitter, also tracked as TA397, is targeting organizations across South Asia with an upgraded version of its custom remote access Trojan, PapRAT, FortiGuard Labs reported on November 2, 2026. Active since at least 2013 and linked to India, Bitter has historically gone after government, energy, and engineering targets.
Bitter rewrote PapRAT in Rust, moving it off C++ and adding PowerShell execution plus sleep and exit commands for 11 in total. The group runs three infection chains built on legitimate Windows features. One abuses ftp.exe and scheduled tasks without deploying any malware binary. In another, PapRAT pulls down a second implant, WmRAT.
Sectigo senior fellow Jason Soroko notes that wiping PapRAT from that chain’s victims may leave the attackers inside, so defenders should also hunt for leftover scripts, scheduled tasks, and extra payloads.
Source: Dark Reading
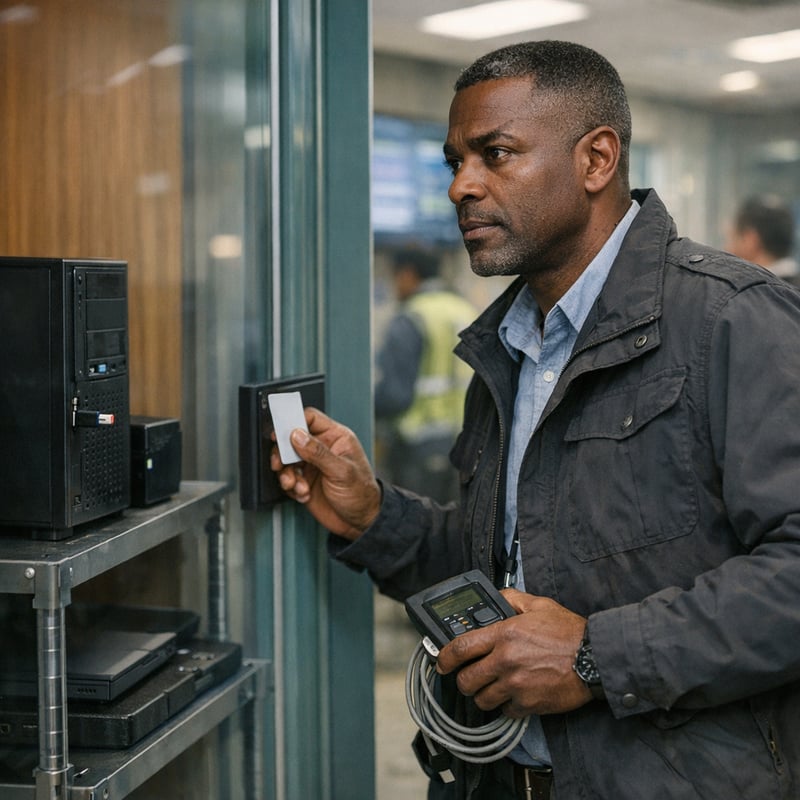
Hackers remotely raised fridge and freezer temperatures, in some cases to 50°C, at supermarkets in seven EU countries overnight on November 1 to 2, 2026, three weeks after a similar attack hit about 700 stores in France. Affected chains include Carrefour, Intermarché, Delhaize, Ikea, ICA, Coop, Kesko, and SuperValu, which pulled chilled and frozen food from 13 stores.
EU Agriculture Commissioner Christophe Hansen called the attacks “a deliberate attempt to disrupt our food supply chain.” No group has claimed responsibility, and it isn’t established whether the incidents are connected. Sophos threat intelligence director Rafe Pilling sees state-backed signaling or a lone hacker as the likeliest explanations.
The attack needed no malware, leaving investigators little to trace. ICA says its systems came from Danfoss, whose end-of-life controllers were hit in France, and Coop says some fridges ran over a more exposed 4G link. Belgian refrigeration firm Sabcobel says patching since the French attack kept the damage from being worse.
Source: The Guardian
Hackers remotely raised fridge and freezer temperatures, in some cases to 50°C, at supermarkets in seven EU countries overnight on November 1 to 2, 2026, three weeks after a similar attack hit about 700 stores in France. Affected chains include Carrefour, Intermarché, Delhaize, Ikea, ICA, Coop, Kesko, and SuperValu, which pulled chilled and frozen food from 13 stores.
EU Agriculture Commissioner Christophe Hansen called the attacks “a deliberate attempt to disrupt our food supply chain.” No group has claimed responsibility, and it isn’t established whether the incidents are connected. Sophos threat intelligence director Rafe Pilling sees state-backed signaling or a lone hacker as the likeliest explanations.
The attack needed no malware, leaving investigators little to trace. ICA says its systems came from Danfoss, whose end-of-life controllers were hit in France, and Coop says some fridges ran over a more exposed 4G link. Belgian refrigeration firm Sabcobel says patching since the French attack kept the damage from being worse.
Source: The Guardian
A pre-authentication flaw in TightVNC Viewer lets a malicious VNC server execute code on a Windows PC during connection setup, before the viewer ever reaches a password check. SeongJoon Cho of SSD Labs Korea found the bug, and SSD Secure Disclosure published proof-of-concept exploit code on October 29, 2026, tested against version 2.8.88 x64. TightVNC Server isn’t affected.
The viewer stores the remote screen’s memory size in a 32-bit integer, so an oversized screen gets a buffer far too small, and later screen updates overwrite neighboring memory. Attackers get in two ways: a user connects to their server, or a viewer sits in Listening Mode on TCP port 5500, where any server can connect.
TightVNC 2.8.89 and 2.8.90 fix the flaw, and the vendor recommends 2.8.90. Install it wherever the viewer runs. Until then, keep Listening Mode off unless a session needs it, firewall port 5500 from untrusted networks, and connect only to VNC servers you know.
Source: Cybersecurity News
A pre-authentication flaw in TightVNC Viewer lets a malicious VNC server execute code on a Windows PC during connection setup, before the viewer ever reaches a password check. SeongJoon Cho of SSD Labs Korea found the bug, and SSD Secure Disclosure published proof-of-concept exploit code on October 29, 2026, tested against version 2.8.88 x64. TightVNC Server isn’t affected.
The viewer stores the remote screen’s memory size in a 32-bit integer, so an oversized screen gets a buffer far too small, and later screen updates overwrite neighboring memory. Attackers get in two ways: a user connects to their server, or a viewer sits in Listening Mode on TCP port 5500, where any server can connect.
TightVNC 2.8.89 and 2.8.90 fix the flaw, and the vendor recommends 2.8.90. Install it wherever the viewer runs. Until then, keep Listening Mode off unless a session needs it, firewall port 5500 from untrusted networks, and connect only to VNC servers you know.
Source: Cybersecurity News
Cursor says maliciously modified versions of Anthropic’s Claude Code extension, 2.1.312 and 2.1.313, sat in its VS Code Extension Marketplace for just over 11 hours on October 29, 2026, affecting at most 5,000 Windows and macOS users. Anthropic didn’t build them, and Cursor has no evidence that other versions or the official distribution were hit.
The code sent the attacker host details such as username, Git email, and public IP, then added an attacker-controlled SSH key and installed scripts that keep retrying the connection. The step that would let the attacker log in failed except where Cursor ran with admin rights. Cursor has since helped take the attacker’s server offline.
Cursor pulled the packages and rebuilt the marketplace. Users who installed either version should update to 2.1.314 and check their SSH authorized keys for one labeled svc-telemetry. Where it appears, isolate the machine, run Cursor’s cleanup script, since uninstalling may leave scripts running, and rotate credentials from a trusted system.
Source: Cyber Security News
Cursor says maliciously modified versions of Anthropic’s Claude Code extension, 2.1.312 and 2.1.313, sat in its VS Code Extension Marketplace for just over 11 hours on October 29, 2026, affecting at most 5,000 Windows and macOS users. Anthropic didn’t build them, and Cursor has no evidence that other versions or the official distribution were hit.
The code sent the attacker host details such as username, Git email, and public IP, then added an attacker-controlled SSH key and installed scripts that keep retrying the connection. The step that would let the attacker log in failed except where Cursor ran with admin rights. Cursor has since helped take the attacker’s server offline.
Cursor pulled the packages and rebuilt the marketplace. Users who installed either version should update to 2.1.314 and check their SSH authorized keys for one labeled svc-telemetry. Where it appears, isolate the machine, run Cursor’s cleanup script, since uninstalling may leave scripts running, and rotate credentials from a trusted system.
Source: Cyber Security News
Binance has replaced 90% of the $6.3 billion stolen on October 29, 2026, in what’s believed to be crypto’s largest hack, ahead of the $1.5 billion Bybit theft in 2025. Using more than $6.34 billion in company funds, it has fully covered bitcoin, Ethereum, and Tether holdings. The last 10%, in less-liquid tokens, will take longer to buy.
The FBI has blamed North Korea, naming the state-backed group it tracks as TraderTraitor, part of the Lazarus Group. It says the hackers are converting the stolen assets into Ethereum ahead of further laundering. Binance has frozen about $3 billion of those assets with law enforcement and industry partners.
Binance’s early investigation pointed to a compromised engineer’s laptop, though it has since found “additional points of breach.” Co-CEO Richard Teng says more than one attacker took part, using a “self-destruct mechanism” to cover the intrusion. Withdrawals began resuming on several networks on November 1.
Source: BBC News
Binance has replaced 90% of the $6.3 billion stolen on October 29, 2026, in what’s believed to be crypto’s largest hack, ahead of the $1.5 billion Bybit theft in 2025. Using more than $6.34 billion in company funds, it has fully covered bitcoin, Ethereum, and Tether holdings. The last 10%, in less-liquid tokens, will take longer to buy.
The FBI has blamed North Korea, naming the state-backed group it tracks as TraderTraitor, part of the Lazarus Group. It says the hackers are converting the stolen assets into Ethereum ahead of further laundering. Binance has frozen about $3 billion of those assets with law enforcement and industry partners.
Binance’s early investigation pointed to a compromised engineer’s laptop, though it has since found “additional points of breach.” Co-CEO Richard Teng says more than one attacker took part, using a “self-destruct mechanism” to cover the intrusion. Withdrawals began resuming on several networks on November 1.
Source: BBC News
Attackers started targeting a no-login remote code execution flaw in WordPress’s core updater nine minutes after Wordfence deployed a firewall rule for it on October 28, 2026, the day WordPress 7.1.4 shipped the fix. By October 30, Wordfence was blocking more than 60,000 attempts in any 24 hours. It has reported no confirmed compromises.
The flaw, CVE-2026-119977 (CVSS 8.1, High), affects versions 4.7 through 7.1.3. Predictable temporary folder names let an attacker reach a staged installer during a full core update. The window usually lasts seconds, and wp-content/upgrade/ must be reachable from the web.
Admins should update to 7.1.4, or their branch’s patched release back to 4.7.39, and confirm it installed rather than trust automatic updates; 4.6 and earlier get no fix. Paid Wordfence customers have the rule, but free users wait until November 27. Meanwhile, block web access to wp-content/upgrade/; plugin firewalls only catch this when set to load before WordPress.
Source: Cybersecurity News
Attackers started targeting a no-login remote code execution flaw in WordPress’s core updater nine minutes after Wordfence deployed a firewall rule for it on October 28, 2026, the day WordPress 7.1.4 shipped the fix. By October 30, Wordfence was blocking more than 60,000 attempts in any 24 hours. It has reported no confirmed compromises.
The flaw, CVE-2026-119977 (CVSS 8.1, High), affects versions 4.7 through 7.1.3. Predictable temporary folder names let an attacker reach a staged installer during a full core update. The window usually lasts seconds, and wp-content/upgrade/ must be reachable from the web.
Admins should update to 7.1.4, or their branch’s patched release back to 4.7.39, and confirm it installed rather than trust automatic updates; 4.6 and earlier get no fix. Paid Wordfence customers have the rule, but free users wait until November 27. Meanwhile, block web access to wp-content/upgrade/; plugin firewalls only catch this when set to load before WordPress.
Source: Cybersecurity News
A hacktivist group calling itself the Department of Peace has leaked records on more than 41,000 DHS employees and contractors, including ICE and CBP personnel and federal cybersecurity staff. Transparency collective DDoSecrets published the database, dubbed Icepick, on October 28, 2026, alongside a searchable version. It holds names, roles, and work contact details, but no home addresses, DDoSecrets says.
The group says it took the data from an Okta single sign-on service DHS uses, but Okta says it has no evidence its systems were compromised. The hacktivists framed the leak as payback for DHS Secretary Markwayne Mullin’s July 17 pledge to step up immigration enforcement.
Icepick also lists more than 55,000 internal access groups, some referencing surveillance platform PenLink and AI tools such as ChatGPT and Gemini. DHS says it is aware of a potential breach and working to address it.
Source: CNET
A hacktivist group calling itself the Department of Peace has leaked records on more than 41,000 DHS employees and contractors, including ICE and CBP personnel and federal cybersecurity staff. Transparency collective DDoSecrets published the database, dubbed Icepick, on October 28, 2026, alongside a searchable version. It holds names, roles, and work contact details, but no home addresses, DDoSecrets says.
The group says it took the data from an Okta single sign-on service DHS uses, but Okta says it has no evidence its systems were compromised. The hacktivists framed the leak as payback for DHS Secretary Markwayne Mullin’s July 17 pledge to step up immigration enforcement.
Icepick also lists more than 55,000 internal access groups, some referencing surveillance platform PenLink and AI tools such as ChatGPT and Gemini. DHS says it is aware of a potential breach and working to address it.
Source: CNET
Polymarket’s international platform halted trading on October 29, 2026, after a supply chain attack drained user funds. The company hasn’t disclosed losses, but the wallet believed to belong to the attacker held about $2.65 million, according to Arkham data. Researchers trace the malicious JavaScript to DebugBear, a UK firm that monitors website performance, through its real user monitoring script.
The code targeted logged-in users, selling positions or transferring tokens directly to an attacker-controlled wallet. DebugBear confirmed it was dealing with a security incident and told customers to remove its script. Polymarket, which hasn’t named the vendor, referred the breach to law enforcement and pledged to make every affected trader whole. Trading restarted roughly an hour later.
Polymarket’s US exchange appears to have been untouched. This is the company’s second third-party breach in months — a similar attack in June 2026 cost traders a reported $3 million.
Source: SecurityWeek
Polymarket’s international platform halted trading on October 29, 2026, after a supply chain attack drained user funds. The company hasn’t disclosed losses, but the wallet believed to belong to the attacker held about $2.65 million, according to Arkham data. Researchers trace the malicious JavaScript to DebugBear, a UK firm that monitors website performance, through its real user monitoring script.
The code targeted logged-in users, selling positions or transferring tokens directly to an attacker-controlled wallet. DebugBear confirmed it was dealing with a security incident and told customers to remove its script. Polymarket, which hasn’t named the vendor, referred the breach to law enforcement and pledged to make every affected trader whole. Trading restarted roughly an hour later.
Polymarket’s US exchange appears to have been untouched. This is the company’s second third-party breach in months — a similar attack in June 2026 cost traders a reported $3 million.
Source: SecurityWeek
A surprisingly clumsy phishing campaign impersonating Anthropic has been bypassing Proofpoint’s Secure Email Gateway and Microsoft Defender for Office 365 since September 2026, Cofense researchers found. Attackers send fake “private preview” invites to an Anthropic AI tool from a legitimate GoTo Webinar address, then route victims through a fake Zoom page to steal Google or Microsoft logins.
The emails carry a misspelled sender name (“Austin from nthropic”), a grammatical error in the subject line, and zero Anthropic branding. The theft flow is half-broken, too: the Google path never asks for a password. Since October 28, the attackers have swapped the Zoom page for a fake Anthropic one.
Yet Cofense points to three simple tricks that may explain the bypass: a sender address open to every GoTo Webinar account holder, Zapier-shortened links, and two CAPTCHAs that keep scanners and VPNs from following the chain. Keeper Security chief information security officer Shane Barney argues email gateways will always have blind spots, so defenses should focus on identity, including phishing-resistant multifactor authentication.
Source: Dark Reading
A surprisingly clumsy phishing campaign impersonating Anthropic has been bypassing Proofpoint’s Secure Email Gateway and Microsoft Defender for Office 365 since September 2026, Cofense researchers found. Attackers send fake “private preview” invites to an Anthropic AI tool from a legitimate GoTo Webinar address, then route victims through a fake Zoom page to steal Google or Microsoft logins.
The emails carry a misspelled sender name (“Austin from nthropic”), a grammatical error in the subject line, and zero Anthropic branding. The theft flow is half-broken, too: the Google path never asks for a password. Since October 28, the attackers have swapped the Zoom page for a fake Anthropic one.
Yet Cofense points to three simple tricks that may explain the bypass: a sender address open to every GoTo Webinar account holder, Zapier-shortened links, and two CAPTCHAs that keep scanners and VPNs from following the chain. Keeper Security chief information security officer Shane Barney argues email gateways will always have blind spots, so defenses should focus on identity, including phishing-resistant multifactor authentication.
Source: Dark Reading
Hackers broke into Florida’s student financial aid website, compromising personal information including Social Security numbers, the Florida Department of Education (FLDOE) confirmed. The department says the breach may have affected about 4.9 million people and appears limited to FloridaStudentFinancialAidSG.org.
The FLDOE discovered the breach on October 19 and immediately moved to stop the unauthorized access, but hasn’t said how long the attackers were inside. It has notified Florida’s Attorney General, as state law requires, and is working with the Florida Digital Service and the Florida Department of Law Enforcement, which has opened a criminal investigation.
One bit of relief: officials say financial aid is safe — disbursements, tuition payments, scholarships, grants, and student loan eligibility won’t be affected. The FLDOE is urging anyone affected to monitor their financial accounts and credit reports, and warns the aid website may see temporary disruptions during the response.
Source: CBS News Miami
Hackers broke into Florida’s student financial aid website, compromising personal information including Social Security numbers, the Florida Department of Education (FLDOE) confirmed. The department says the breach may have affected about 4.9 million people and appears limited to FloridaStudentFinancialAidSG.org.
The FLDOE discovered the breach on October 19 and immediately moved to stop the unauthorized access, but hasn’t said how long the attackers were inside. It has notified Florida’s Attorney General, as state law requires, and is working with the Florida Digital Service and the Florida Department of Law Enforcement, which has opened a criminal investigation.
One bit of relief: officials say financial aid is safe — disbursements, tuition payments, scholarships, grants, and student loan eligibility won’t be affected. The FLDOE is urging anyone affected to monitor their financial accounts and credit reports, and warns the aid website may see temporary disruptions during the response.
Source: CBS News Miami