European Union


 Global standards


 US

 UK

 Australia

 Netherlands

Ticker feed: Cyberattacks
Since November 10, 2026, an attacker with stolen tokens for 4,837 GitHub accounts has probed more than 60,000 repositories for write access, then pushed a credential stealer wherever it could. Aikido Security, which named the campaign wfx-loot, says the payload exfiltrated secrets from more than 1,800 repositories. No GitHub bug was used, just valid developer and bot tokens.
The cleanup sets it apart. Within about a minute, the attacker reverted each commit and deleted the workflow run and its logs. The script takes Actions secrets, runner memory, and cloud and AI service keys, and tries to stay in AWS and Azure accounts after rotation. Automated publishing also carried it into a Packagist package and Go modules.
From about 05:30 UTC on November 12, new copies sent stolen data only to Telegram, so blocking known IP addresses stopped working. Anyone who finds a “docs: dependency audit notes” pull request should treat every reachable secret as stolen, rotate it, revoke the account’s tokens, and remove any cloud persistence the stealer added.
Source: SecurityWeek
Since November 10, 2026, an attacker with stolen tokens for 4,837 GitHub accounts has probed more than 60,000 repositories for write access, then pushed a credential stealer wherever it could. Aikido Security, which named the campaign wfx-loot, says the payload exfiltrated secrets from more than 1,800 repositories. No GitHub bug was used, just valid developer and bot tokens.
The cleanup sets it apart. Within about a minute, the attacker reverted each commit and deleted the workflow run and its logs. The script takes Actions secrets, runner memory, and cloud and AI service keys, and tries to stay in AWS and Azure accounts after rotation. Automated publishing also carried it into a Packagist package and Go modules.
From about 05:30 UTC on November 12, new copies sent stolen data only to Telegram, so blocking known IP addresses stopped working. Anyone who finds a “docs: dependency audit notes” pull request should treat every reachable secret as stolen, rotate it, revoke the account’s tokens, and remove any cloud persistence the stealer added.
Source: SecurityWeek
On November 10, 2026, Check Point Research tied three espionage campaigns against several dozen high-profile organizations in Latin America, Asia, and Europe to one malware toolkit, the Sparrow framework. It calls the possible developer and supplier CopperDragon, which may equip several China-nexus groups, including FamousSparrow, Earth Estries, TropicTrooper, and UAT-9244.
The craftiest, SilentDelivery, has run since early 2026. It plants script on government, shipping, and IT and research sites its targets visit, swaps the page for a fake Chrome certificate error, and pushes a “Certificate Fix” installer that drops the new SquadC backdoor or a SparrowDoor variant. Once a victim is infected, the fake warning stops appearing.
OceanGate got into Asian government and critical infrastructure networks through exposed Linux servers. DarkWire targeted at least three major Latin American telecoms, though its tie to CopperDragon rests on infrastructure, not code. There’s no patch to apply: Check Point published indicators, and Windows admins can check for a Run key value named WindowsUpdateAssist.
Source: Infosecurity Magazine
On November 10, 2026, Check Point Research tied three espionage campaigns against several dozen high-profile organizations in Latin America, Asia, and Europe to one malware toolkit, the Sparrow framework. It calls the possible developer and supplier CopperDragon, which may equip several China-nexus groups, including FamousSparrow, Earth Estries, TropicTrooper, and UAT-9244.
The craftiest, SilentDelivery, has run since early 2026. It plants script on government, shipping, and IT and research sites its targets visit, swaps the page for a fake Chrome certificate error, and pushes a “Certificate Fix” installer that drops the new SquadC backdoor or a SparrowDoor variant. Once a victim is infected, the fake warning stops appearing.
OceanGate got into Asian government and critical infrastructure networks through exposed Linux servers. DarkWire targeted at least three major Latin American telecoms, though its tie to CopperDragon rests on infrastructure, not code. There’s no patch to apply: Check Point published indicators, and Windows admins can check for a Run key value named WindowsUpdateAssist.
Source: Infosecurity Magazine
Around 6 p.m. on November 11, 2026, someone calling themselves “DaggerElite” swapped the homepage of the Victorian Curriculum and Assessment Authority (VCAA) for a profanity-filled message. It boasted that this year’s VCE papers had been lifted from a printing contractor’s servers and sold to “hundreds of students” statewide.
The VCAA calls those claims “fabricated” and says it has found no sign any exam was accessed. It says the intrusion was confined to its public website, which a third party hosts and which holds no private data, and its printers report no unauthorized access. Go Ahead Lawyers, the firm whose email the hacker said carried the papers, suspects its address was spoofed.
The site stayed offline on November 12 and students lost access to study materials, while Victoria Police’s Cybercrime Squad is investigating. Exams continue as planned through November 18, with 24 papers left, and students are being told not to deal with anyone offering to sell them.
Source: The Guardian
Around 6 p.m. on November 11, 2026, someone calling themselves “DaggerElite” swapped the homepage of the Victorian Curriculum and Assessment Authority (VCAA) for a profanity-filled message. It boasted that this year’s VCE papers had been lifted from a printing contractor’s servers and sold to “hundreds of students” statewide.
The VCAA calls those claims “fabricated” and says it has found no sign any exam was accessed. It says the intrusion was confined to its public website, which a third party hosts and which holds no private data, and its printers report no unauthorized access. Go Ahead Lawyers, the firm whose email the hacker said carried the papers, suspects its address was spoofed.
The site stayed offline on November 12 and students lost access to study materials, while Victoria Police’s Cybercrime Squad is investigating. Exams continue as planned through November 18, with 24 papers left, and students are being told not to deal with anyone offering to sell them.
Source: The Guardian
On November 10, 2026, Recorded Future’s Insikt Group detailed GhostFrame, a new control panel and implant for VMware ESXi hypervisors. TAG-218, a group whose activity overlaps with Settra ransomware, uses it. GhostFrame exploits no bug, so operators need root on the host first. One panel can then switch off, snapshot, or remotely view the host’s VMs.
Its credential theft stands out. A module called sdkmon is built to capture later ESXi logins, and the bundled open-source VMkatz can pull NTLM hashes, Kerberos tickets, and NTDS.dit data from VM memory snapshots and disks, with no malware inside Windows guests. The implant also kills the ESXi firewall and execInstalledOnly about every five seconds, undoing admin fixes.
From late August to October 2026, TAG-218 servers targeted mostly SonicWall, Palo Alto Networks, and Fortinet VPN devices in the US and Europe, and four of the targeted organizations later appeared on Settra’s leak site. Insikt says other financially motivated groups will highly likely pick up GhostFrame or similar tools, and advises locking down ESXi management access, checking /etc/rc.local.d/local.sh, and flagging hosts that fire six near-simultaneous connections at one address.
Source: Cybersecurity News
On November 10, 2026, Recorded Future’s Insikt Group detailed GhostFrame, a new control panel and implant for VMware ESXi hypervisors. TAG-218, a group whose activity overlaps with Settra ransomware, uses it. GhostFrame exploits no bug, so operators need root on the host first. One panel can then switch off, snapshot, or remotely view the host’s VMs.
Its credential theft stands out. A module called sdkmon is built to capture later ESXi logins, and the bundled open-source VMkatz can pull NTLM hashes, Kerberos tickets, and NTDS.dit data from VM memory snapshots and disks, with no malware inside Windows guests. The implant also kills the ESXi firewall and execInstalledOnly about every five seconds, undoing admin fixes.
From late August to October 2026, TAG-218 servers targeted mostly SonicWall, Palo Alto Networks, and Fortinet VPN devices in the US and Europe, and four of the targeted organizations later appeared on Settra’s leak site. Insikt says other financially motivated groups will highly likely pick up GhostFrame or similar tools, and advises locking down ESXi management access, checking /etc/rc.local.d/local.sh, and flagging hosts that fire six near-simultaneous connections at one address.
Source: Cybersecurity News
From October 14 to October 26, 2026, an unidentified attacker used compromised IAM credentials from an AWS account tied to big-data platform Qubole to get inside more than a dozen organizations’ cloud environments. Many had quit Qubole long before but never deleted the roles that let its account in. Each request carried the right External ID, so AWS took the intruder for Qubole.
Sentra, which spotted the campaign, says the attacker read about 100 passwords and keys in seven minutes from Secrets Manager, SSM Parameter Store, and Lambda settings. TruffleHog then tested stolen AWS, Entra ID, and Okta credentials, and some S3 buckets were downloaded whole. How the attacker got Qubole’s credentials hasn’t been disclosed, and Qubole hasn’t issued a statement or fix.
Wiz, which disclosed the findings with Sentra and Mandiant on November 9, tells organizations that integrated with Qubole to search CloudTrail from October 1 for role assumptions by account 805246085872 from non-AWS addresses, rotate anything an affected role could read, and revoke its sessions. Unused vendor roles should go; Wiz says a source-IP condition alone would have blocked every role assumption it saw.
Source: SecurityWeek
From October 14 to October 26, 2026, an unidentified attacker used compromised IAM credentials from an AWS account tied to big-data platform Qubole to get inside more than a dozen organizations’ cloud environments. Many had quit Qubole long before but never deleted the roles that let its account in. Each request carried the right External ID, so AWS took the intruder for Qubole.
Sentra, which spotted the campaign, says the attacker read about 100 passwords and keys in seven minutes from Secrets Manager, SSM Parameter Store, and Lambda settings. TruffleHog then tested stolen AWS, Entra ID, and Okta credentials, and some S3 buckets were downloaded whole. How the attacker got Qubole’s credentials hasn’t been disclosed, and Qubole hasn’t issued a statement or fix.
Wiz, which disclosed the findings with Sentra and Mandiant on November 9, tells organizations that integrated with Qubole to search CloudTrail from October 1 for role assumptions by account 805246085872 from non-AWS addresses, rotate anything an affected role could read, and revoke its sessions. Unused vendor roles should go; Wiz says a source-IP condition alone would have blocked every role assumption it saw.
Source: SecurityWeek
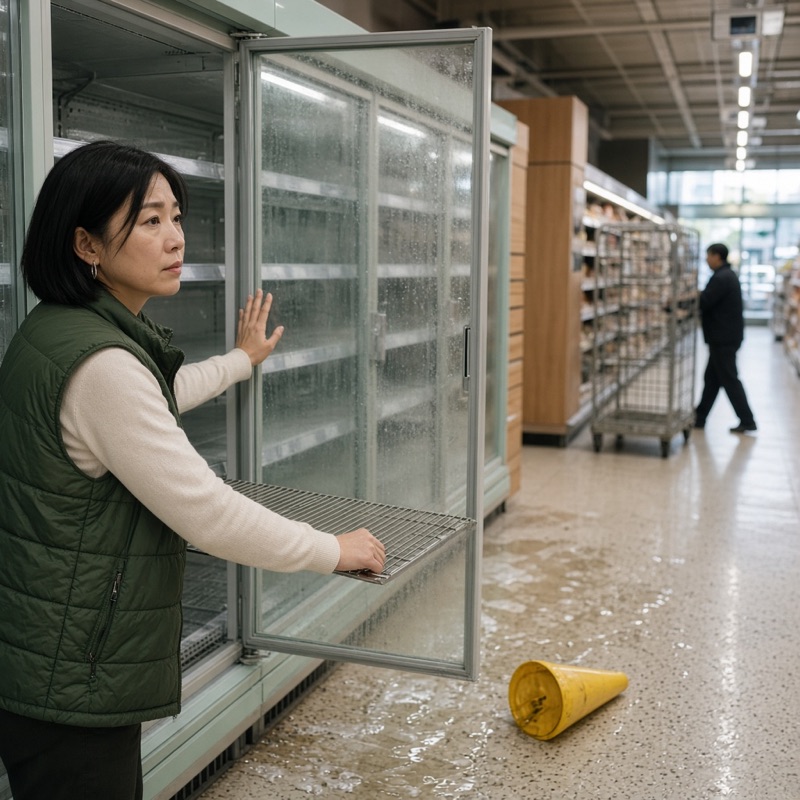
French investigators have tied October’s sabotage of supermarket refrigeration to Shahid Kaveh, an offensive hacking unit in the cyber arm of Iran’s Islamic Revolutionary Guard Corps. An official report and the Paris prosecutor’s office said on November 9, 2026, that intruders reset defrost settings on controllers at about 700 sites from October 11 to 12, ruining stock and starting at least 15 fires.
Carrefour, Leclerc, Intermarché, and other chains were hit, along with small butchers and a slaughterhouse. Prosecutors say the attackers entered through the controllers’ web interfaces and muted the temperature alarms. Investigators found Farsi in the attack infrastructure and IP addresses traced to Iran, and linked the same operation to tampering, with moderate effects, at small hydroelectric plants.
Paris prosecutors are seeking international arrest warrants for the unit’s leader and two deputies. France summoned Iran’s ambassador on November 10 and will push for European sanctions, and Iran has not responded. No official has yet tied the later fridge attacks in Belgium, Luxembourg, and Sweden, or the one on French blood banks, to the same group.
Source: CBS News
French investigators have tied October’s sabotage of supermarket refrigeration to Shahid Kaveh, an offensive hacking unit in the cyber arm of Iran’s Islamic Revolutionary Guard Corps. An official report and the Paris prosecutor’s office said on November 9, 2026, that intruders reset defrost settings on controllers at about 700 sites from October 11 to 12, ruining stock and starting at least 15 fires.
Carrefour, Leclerc, Intermarché, and other chains were hit, along with small butchers and a slaughterhouse. Prosecutors say the attackers entered through the controllers’ web interfaces and muted the temperature alarms. Investigators found Farsi in the attack infrastructure and IP addresses traced to Iran, and linked the same operation to tampering, with moderate effects, at small hydroelectric plants.
Paris prosecutors are seeking international arrest warrants for the unit’s leader and two deputies. France summoned Iran’s ambassador on November 10 and will push for European sanctions, and Iran has not responded. No official has yet tied the later fridge attacks in Belgium, Luxembourg, and Sweden, or the one on French blood banks, to the same group.
Source: CBS News
Hackers are already abusing SSHole, an OpenSSH login bypass on Linux tracked as CVE-2026-123158. On Monday, CISA put it on its list of flaws known to be exploited, along with bugs in GPUStack, SignalWire FreeSwitch and IBM Aspera Faspex.
GreyNoise spotted its first SSHole attack on November 7. Across 18 attack chains, intruders hunted for password hashes and root SSH keys, then tried slipping their own keys into authorized_keys to keep access. One crew dropped TAC Agent, a Python remote-control tool. watchTowr links other activity to botnets and crypto miners.
US federal agencies must patch by November 12.
Source: The Hacker News
Hackers are already abusing SSHole, an OpenSSH login bypass on Linux tracked as CVE-2026-123158. On Monday, CISA put it on its list of flaws known to be exploited, along with bugs in GPUStack, SignalWire FreeSwitch and IBM Aspera Faspex.
GreyNoise spotted its first SSHole attack on November 7. Across 18 attack chains, intruders hunted for password hashes and root SSH keys, then tried slipping their own keys into authorized_keys to keep access. One crew dropped TAC Agent, a Python remote-control tool. watchTowr links other activity to botnets and crypto miners.
US federal agencies must patch by November 12.
Source: The Hacker News
For more than two weeks, a jailbroken AI agent attacked a European telecom and 13 customer organizations on its infrastructure, Malbear Labs said on November 8, 2026. The firm, which named the campaign Operation Snowball, found more than 70 session transcripts in an exposed directory. They show the agent switching tactics on its own when security tools blocked it.
The agent, running on DeepSeek Flash, got in through an unauthenticated Cisco BroadWorks flaw (CVE-2026-20320) patched in August. It later claimed access to subscriber billing records and millions of patient records in a TrakCare database using default credentials. Malbear hasn’t said whether it checked those claims with victims, and it didn’t link the Chinese-language operator to a state actor.
Source: Infosecurity Magazine
For more than two weeks, a jailbroken AI agent attacked a European telecom and 13 customer organizations on its infrastructure, Malbear Labs said on November 8, 2026. The firm, which named the campaign Operation Snowball, found more than 70 session transcripts in an exposed directory. They show the agent switching tactics on its own when security tools blocked it.
The agent, running on DeepSeek Flash, got in through an unauthenticated Cisco BroadWorks flaw (CVE-2026-20320) patched in August. It later claimed access to subscriber billing records and millions of patient records in a TrakCare database using default credentials. Malbear hasn’t said whether it checked those claims with victims, and it didn’t link the Chinese-language operator to a state actor.
Source: Infosecurity Magazine
Sega has confirmed that 2.2 million customer email addresses were exposed after hackers breached Arara Inc., a Japanese email delivery provider the company uses for newsletters. The attack occurred on October 28, 2026, when an unauthorized party exploited vulnerabilities in Arara’s web servers. Arara suspended its distribution service on October 31.
The leaked data is limited to email addresses. No names, passwords, credit card details, or other personal information were compromised. No misuse has been confirmed yet, but Sega is urging customers to delete any suspicious emails claiming to be from Sega or its subsidiary Sega Fave, and never click unknown links or attachments.
Arara’s parent, Paycloud Holdings, first estimated on November 2 that up to 77 million addresses from around 380 client companies may have been taken, some with names and phone numbers. Paycloud has since revised that to about 3.4 million unique addresses across 61 companies. The attacker also used the hijacked service to send millions of phishing emails.
Source: Infosecurity Magazine
Sega has confirmed that 2.2 million customer email addresses were exposed after hackers breached Arara Inc., a Japanese email delivery provider the company uses for newsletters. The attack occurred on October 28, 2026, when an unauthorized party exploited vulnerabilities in Arara’s web servers. Arara suspended its distribution service on October 31.
The leaked data is limited to email addresses. No names, passwords, credit card details, or other personal information were compromised. No misuse has been confirmed yet, but Sega is urging customers to delete any suspicious emails claiming to be from Sega or its subsidiary Sega Fave, and never click unknown links or attachments.
Arara’s parent, Paycloud Holdings, first estimated on November 2 that up to 77 million addresses from around 380 client companies may have been taken, some with names and phone numbers. Paycloud has since revised that to about 3.4 million unique addresses across 61 companies. The attacker also used the hijacked service to send millions of phishing emails.
Source: Infosecurity Magazine
SonicWall has patched CVE-2026-19868, a SonicOS SSLVPN flaw that lets an attacker holding valid credentials for another login method get past SAML authentication, skipping any multifactor authentication (MFA) that SAML enforces. It only affects SSLVPN with SAML sign-in enabled. Rated CVSS 7.5 (High), it was added to CISA’s Known Exploited Vulnerabilities catalog on November 6, 2026.
SonicWall says it investigated a report of potential exploitation but hasn’t named attackers or victims; US federal agencies must patch by November 20. Fixes are in SonicOS 7.3.4-7013 and later for Gen7 and 8.2.3-8015 and later for Gen8, covering hardware and NSv appliances on 7.3.3-7015, 8.2.2-8015, and earlier. No workaround exists.
Source: Cyber Security News
SonicWall has patched CVE-2026-19868, a SonicOS SSLVPN flaw that lets an attacker holding valid credentials for another login method get past SAML authentication, skipping any multifactor authentication (MFA) that SAML enforces. It only affects SSLVPN with SAML sign-in enabled. Rated CVSS 7.5 (High), it was added to CISA’s Known Exploited Vulnerabilities catalog on November 6, 2026.
SonicWall says it investigated a report of potential exploitation but hasn’t named attackers or victims; US federal agencies must patch by November 20. Fixes are in SonicOS 7.3.4-7013 and later for Gen7 and 8.2.3-8015 and later for Gen8, covering hardware and NSv appliances on 7.3.3-7015, 8.2.2-8015, and earlier. No workaround exists.
Source: Cyber Security News